Showing posts with label Lazarus Group. Show all posts

Wednesday, December 20, 2017

North Korea Amassing Bitcoin To Fund Cyberattacks According To Crowdstrike CEO


Content originally published at iBankCoin.com


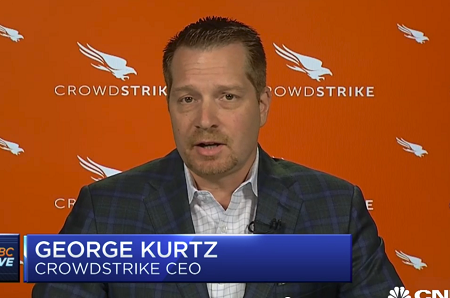
The CEO of cybersecurity firm Crowdstrike, George Kurtz, says North Korea is "absolutely" accumulating a giant pile of bitcoin to fund cyberattacks.

"They"re building a cache of bitcoin, if you think about it. It"s an anonymous currency, it can easily bypass any sort of sanctions because there are none on bitcoin, and the value has increased dramatically," Kurtz told CNBC"s "Squawk Alley." "It"s the perfect currency for North Korea to be hoarding." -CNBC


Can someone say "prohibited country" regulations?


The opinion comes on the heels of an op-ed in the WSJ by Homeland Security advisor Tom Bossert, who says North Korea was behind the WannaCry ransomware hack earlier this year, which demanded ransom in bitcoin.


The U.S. government has assessed with a "very high level of confidence" that a hacking entity known as Lazarus Group, which works on behalf of the North Korean government, carried out the WannaCry attack, said the official, who spoke on condition of anonymity to discuss details of the government"s investigation. -CNBC


The WannaCry hack is said to have cost billions, crippling hospitals, banks and companies around the world - and "highlights the capabilities that North Korea has in cyber," according to Kurtz.


Crowdstrike CEO on 2018 cyber threat outlook from CNBC.


Crowdstrike is the firm which analyzed the DNC servers and determined that Russia hacked them - however the Irvine, CA company came under fire in late 2016 when they had to retract a botched report on Russian hacking of Ukrainian artillery using the same "fancy bear" malware they also say the Kremlin used on the DNC servers.


The government of Ukraine issued a statement after the artillery report came out, calling it Fake News:


In connection with the emergence in some media reports which stated that the alleged “80% howitzer D-30 Armed Forces of Ukraine removed through scrapping Russian Ukrainian hackers software gunners,” Land Forces Command of the Armed Forces of Ukraine informs that the said information is incorrect.


Ministry of Defence of Ukraine asks journalists to publish only verified information received from the competent official sources. Spreading false information leads to increased social tension in society and undermines public confidence in the Armed Forces of Ukraine. –mil.gov.ua (translated) (1.6.2017)


So DHS"s Tom Bossert drops an op-ed on a North Korean hacking operation which only takes Bitcoin, and the CEO of Crowdstrike follows up with a stark warning on Bitcoin hoarding by Pyongyang. 


Follow on Twitter @ZeroPointNow § Subscribe to our YouTube channel


Wednesday, May 24, 2017

WannaCry Attackers Have Links To North Korea's Lazarus Group

Cybersecurity researchers at Symantec say they"ve found linkes between the WannaCry Ransomware attackers was likely carried out by a hacking group with ties to North Korea.


In a blog post, Symantec said the “Tools and infrastructure used in the WannaCry ransomware attacks have strong links to Lazarus, the group that was responsible for the destructive attacks on Sony Pictures and the theft of $81 million from the Bangladesh Central Bank.”


Here"s a summary of links provided by Symantec:


  • Following the first WannaCry attack in February, three pieces of malware linked to Lazarus were discovered on the victim’s network: Trojan.Volgmer and two variants of Backdoor.Destover, the disk-wiping tool used in the Sony Pictures attacks.

  • Trojan.Alphanc, which was used to spread WannaCry in the March and April attacks, is a modified version of Backdoor.Duuzer, which has previously been linked to Lazarus.

  • Trojan.Bravonc used the same IP addresses for command and control as Backdoor.Duuzer and Backdoor.Destover, both of which have been linked to Lazarus.

  • Backdoor.Bravonc has similar code obfuscation as WannaCry and Infostealer.Fakepude (which has been linked to Lazarus).

  • There is shared code between WannaCry and Backdoor.Contopee, which has previously been linked to Lazarus.

Symantec discovered that the WannaCry attackers used some of the same hacking tools that were previousky used in other Lazarus Group attacks. There are also, the group reported, “a number of links between WannaCry itself and Lazarus.”


The WannaCry ransomware, for example, shares some code with a piece of malware that has previously been linked to Lazarus.


Symantec also found that the WannaCry attackers used some of the same network infrastructure as the Lazarus Group. “There are a number of crossovers seen in the C&C servers used in the WannaCry campaigns and by other known Lazarus tools.”


Beginning a week ago Friday, the WannaCry virus infected thousands of computers around the world, threatening to destroy users" data unless a ransom was paid in bitcoin. Ultimately, the group received less than $100,000, and most of the data were destroyed.